CVE-2026-41940 - Critical cPanel Vulnerability Exploited in Mr_Rot13 Backdoor campaign
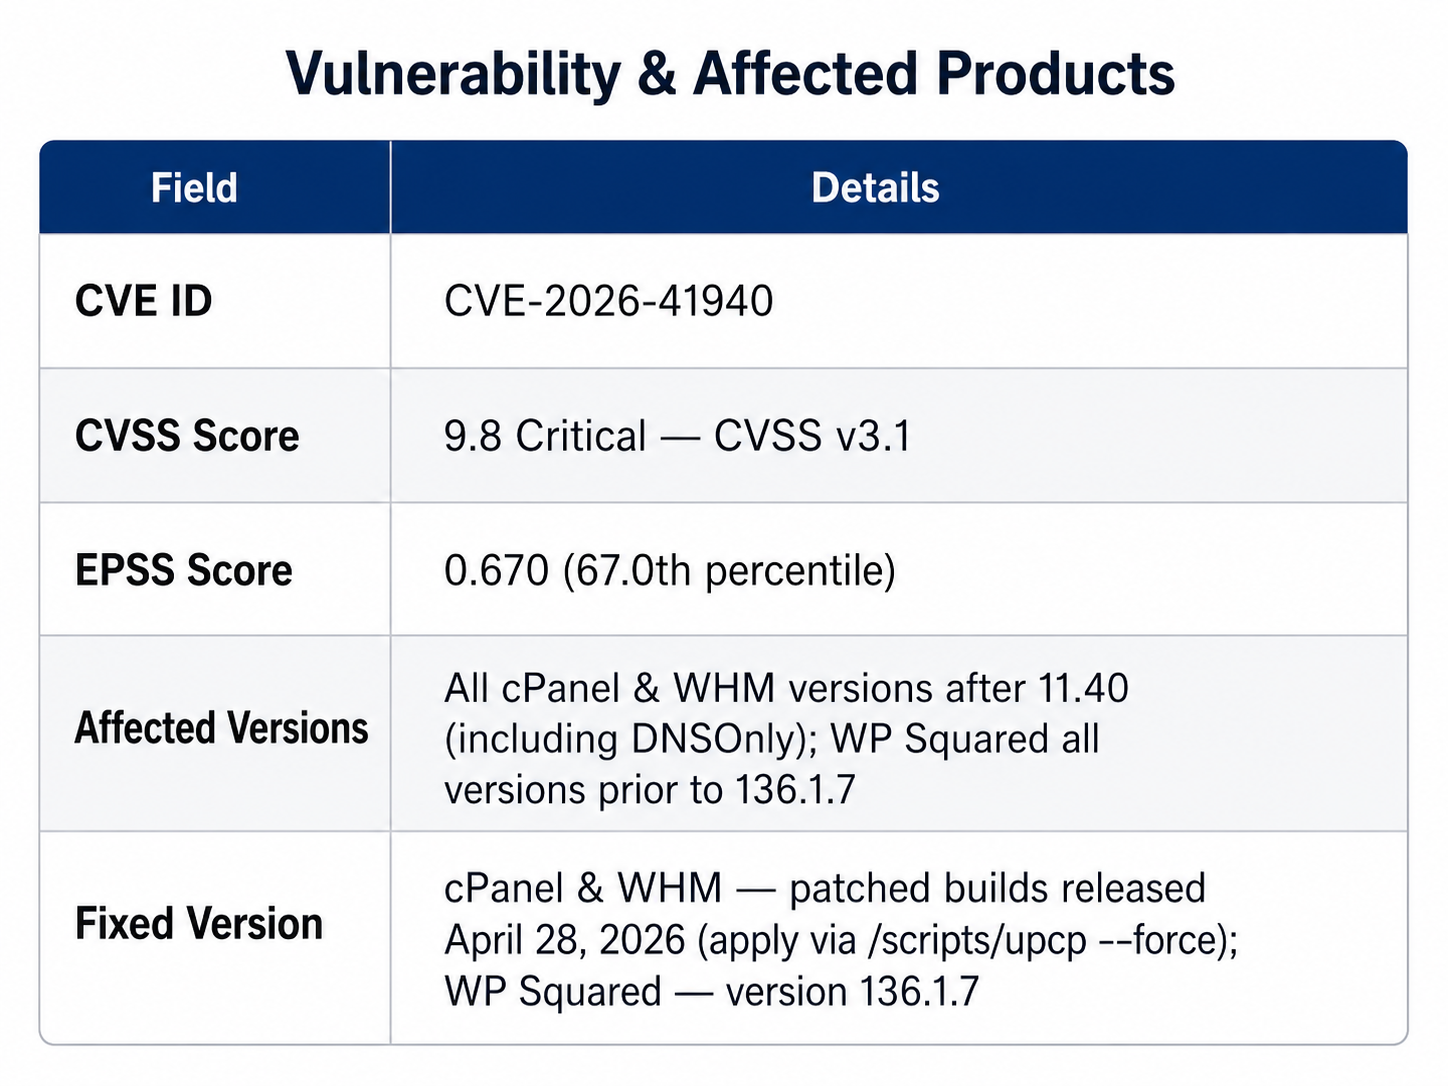
Researchers at QiAnXin XLab have attributed an active exploitation campaign against a critical cPanel authentication bypass vulnerability (CVE-2026-41940) to a long-running threat actor dubbed Mr_Rot13.
The campaign deploys a cross-platform backdoor named Filemanager that steals credentials and establishes persistent access across compromised Linux hosting environments.
More than 2,000 attacker source IPs worldwide have been observed conducting automated attacks against CVE-2026-41940 since its public disclosure on April 28, 2026.
Exploitation activity includes cryptocurrency mining, ransomware deployment, botnet propagation, and backdoor implantation.
Mr_Rot13 & the Filemanager Backdoor
Mr_Rot13 has been operating covertly since at least October 2020, named for their use of the ROT13 cipher to obfuscate C2 addresses and the Telegram handle "0xWR" linked to the group's creator.
Despite six years of continuous activity, their samples and infrastructure maintain near-zero antivirus detections, including a PHP backdoor from 2022 that remains undetected to this day.
Their hallmark is operational discipline: long-lived infrastructure, consistent tooling, and a deliberate preference for stealth over speed.
When an external researcher accidentally interacted with their Telegram bot in May 2026, the group rotated their token within 24 hours.
Their primary payload, Filemanager, is a Go-based cross-platform backdoor with builds for Linux, Windows, and macOS.
It arrives as the final stage of a toolchain that also includes an SSH key implant, a PHP webshell, and a credential-skimming login page, ensuring persistence even if individual components are discovered.
Stolen data is sent simultaneously to an HTTP C2 endpoint and a private Telegram bot, providing a resilient exfiltration channel that survives takedowns. Once running, it exposes a web-based console supporting file management, remote command execution, and shell access.
Attack Methodology: The Automated Infection Chain
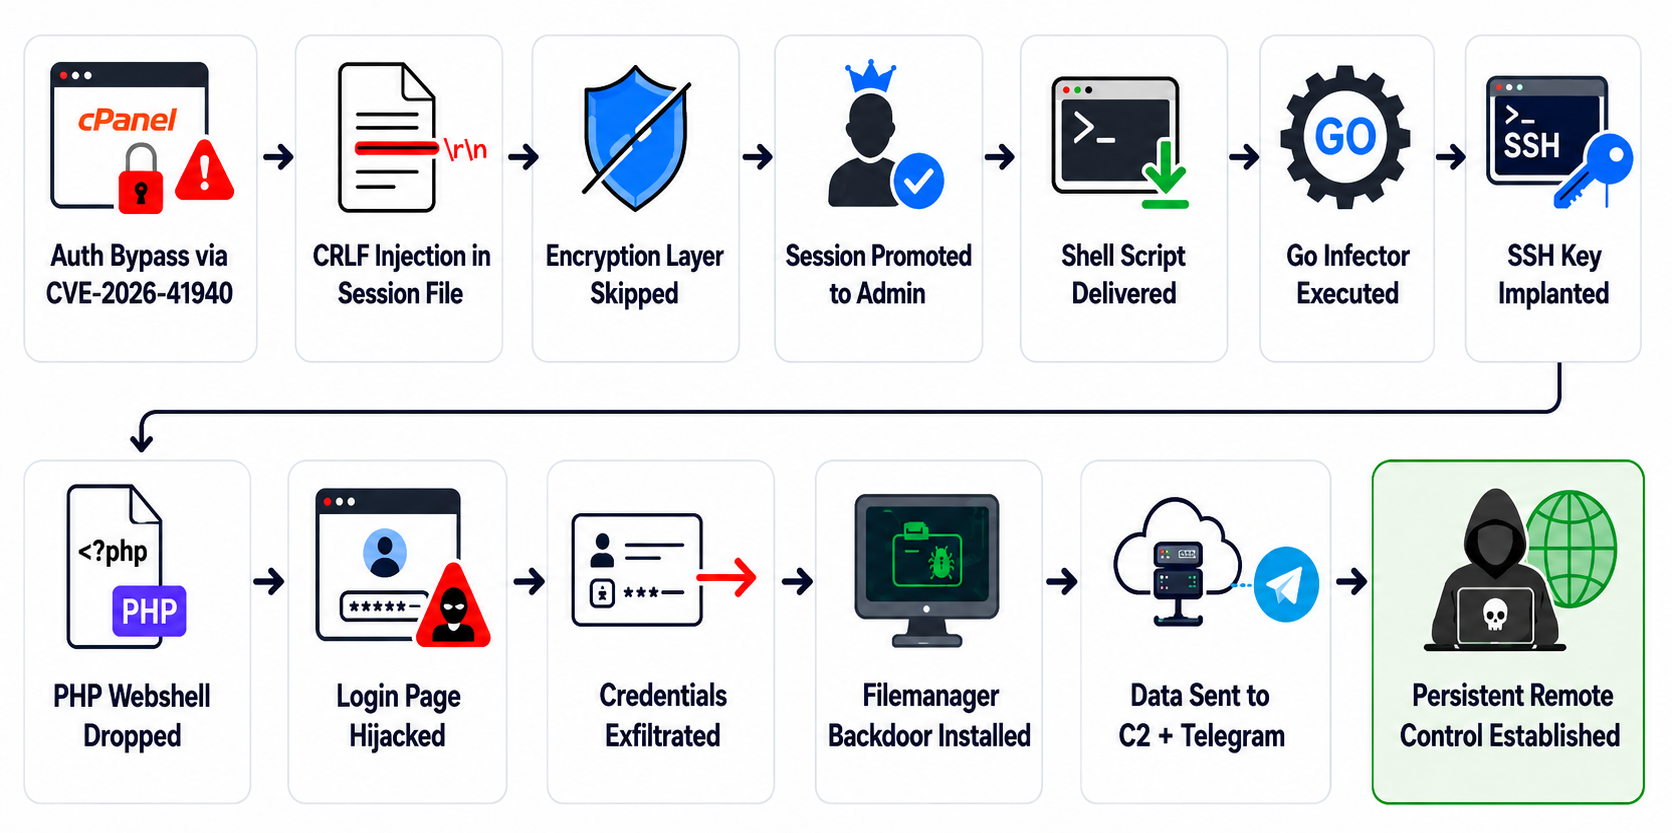
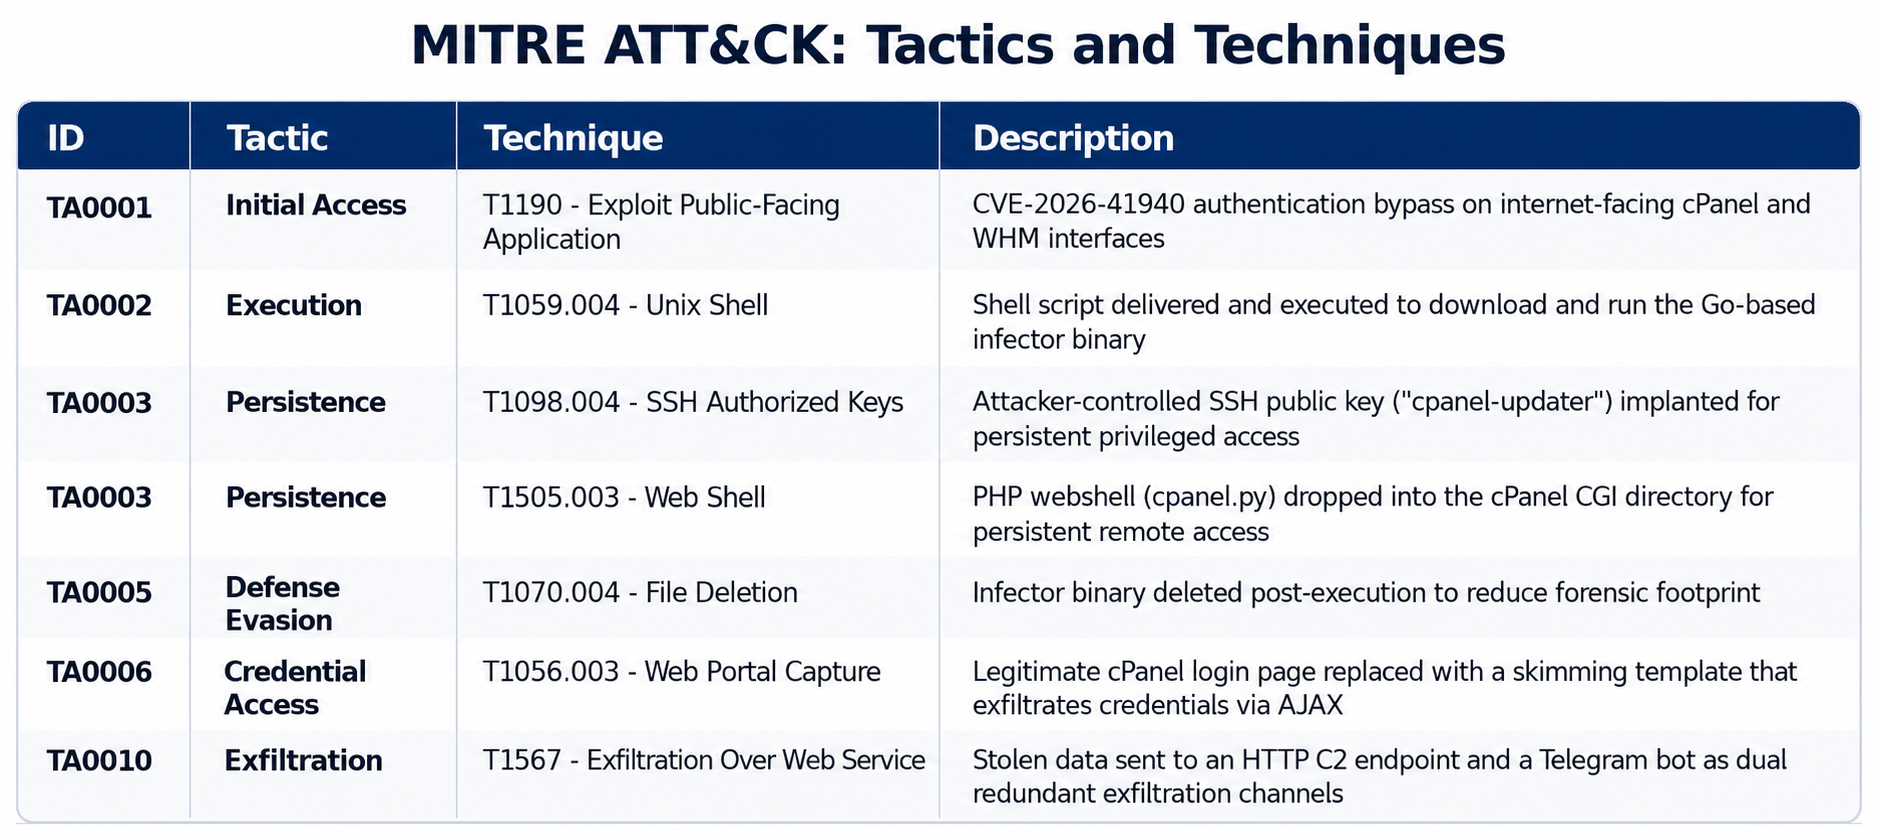
Phase 1: Initial Exploitation: CVE-2026-41940 is abused to bypass cPanel/WHM authentication entirely, no credentials needed, full admin access granted remotely.
Phase 2: Infector Delivery: A shell script downloads and runs a Go-based binary ("Update") from the attacker's server via wget/curl, then deletes itself to avoid detection.
Phase 3: SSH Implantation: The infector hardcodes a new root password and plants an attacker-controlled SSH public key, ensuring persistent privileged access.
Phase 4: Webshell Deployment: A PHP webshell ("cpanel.py") is dropped into the cPanel CGI directory, enabling ongoing file access and remote command execution.
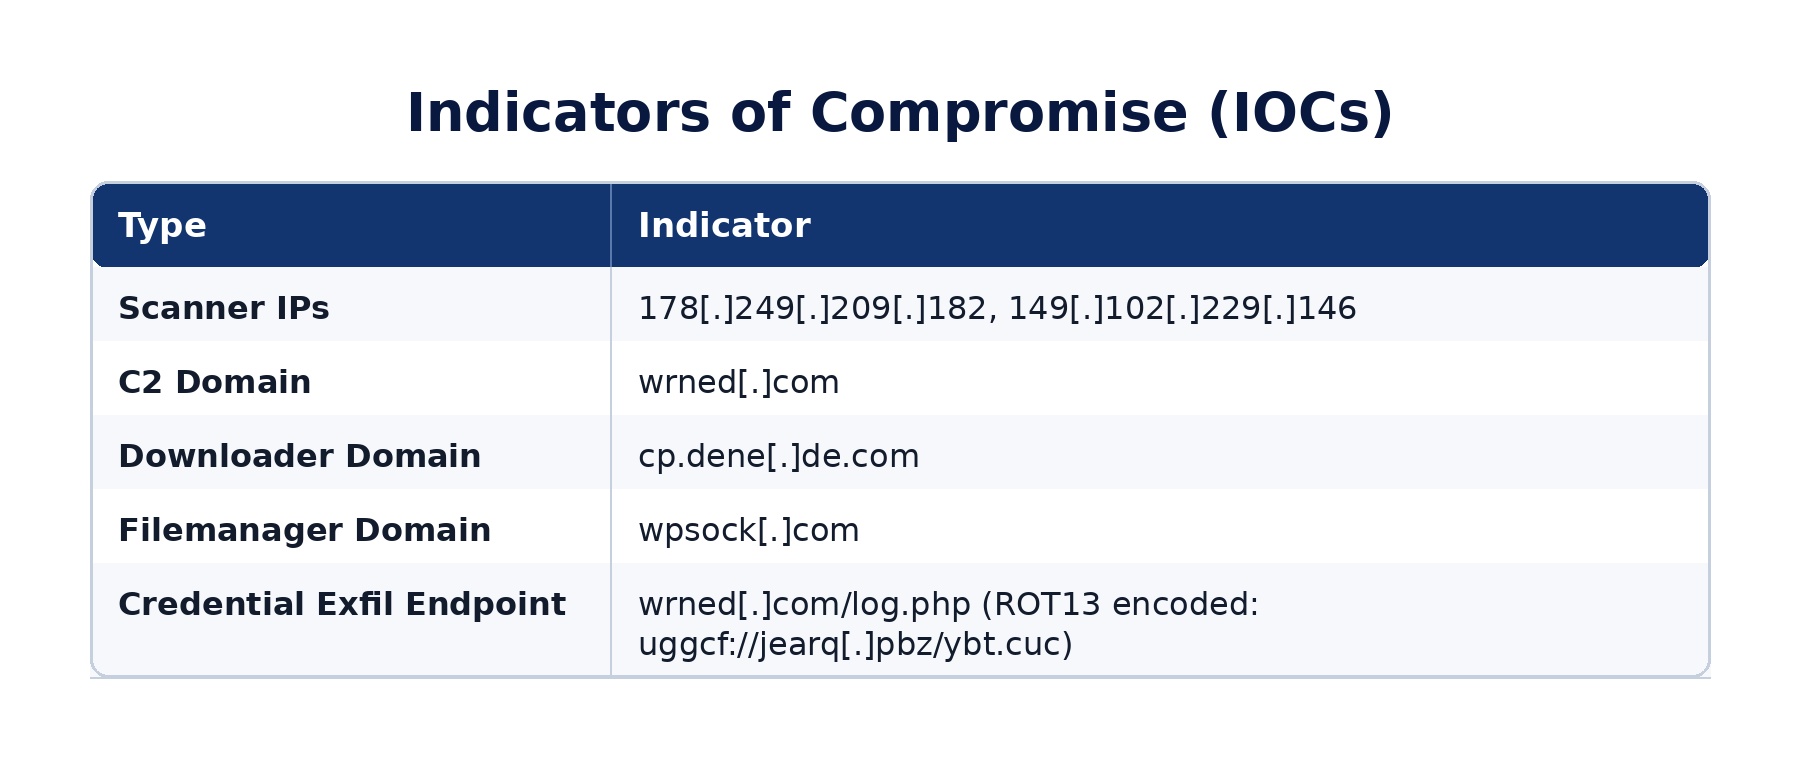
Phase 5: Credential Skimming: Malicious JavaScript replaces the cPanel login page, silently harvesting usernames and passwords and sending them to a ROT13-obfuscated C2.
Phase 6: Filemanager Backdoor: A cross-platform backdoor (Windows/Linux/macOS) is installed from wpsock[.]com, opening a web-based remote-control console on a custom TCP port.
Phase 7: Data Exfiltration: Bash history, SSH keys, database passwords, and valiases are sent to the C2 server and a private Telegram group via dual redundant channels.
Instantly Fix Risks with Saner Patch Management
Saner Patch Management is a continuous, automated, and integrated solution that instantly fixes risks exploited in the wild. It supports major operating systems including Windows, Linux, and macOS, as well as 550+ third-party applications.
It includes a safe testing sandbox to validate patches before production deployment, along with a patch rollback feature in the event of failure or system malfunction, ensuring your infrastructure stays protected without downtime risk.