

Saner Container Orchestration Posture Management (COPM)
Find and Fix Kubernetes Misconfigurations Before They Become Compliance Failures
Saner COPM brings you continuous, benchmark-driven posture management for every Kubernetes cluster, from control plane nodes and worker nodes to namespaces, images, and containers.

How it works
Powered by Prevention & USI
Saner COPM is part of Saner COSP, bringing SecPod’s prevention-first security approach to Kubernetes posture management across on-premises and managed Kubernetes environments.
How it works
Powered by Prevention & USI
Saner COPM is part of Saner COSP, bringing SecPod’s prevention-first security approach to Kubernetes posture management across on-premises and managed Kubernetes environments.
Your first 30 days with Saner
From deployment to measurable risk reduction — here is what to expect.

Full Cluster Configuration Visibility
Every resource across your clusters is mapped against baseline configuration standards from the first scan, so misconfigurations that were previously invisible are immediately on the board.
Compliance Posture Under Control
Custom benchmarks are tuned to specific namespaces and checks, and severity-based evaluation with supporting evidence lets your team work through findings by what actually matters, not a flat list.
Continuous Drift Detection in Place
Resource Trends surface recurring or worsening misconfigurations over time, while Quick Evaluation Benchmarks catch new issues during routine audits rather than waiting for the next full compliance cycle.
Key Features
Everything you need to stay ahead of threats.
Create Tailored Benchmarks
Build benchmarks scoped to exactly the namespace and checks that matter, not one blanket policy for the whole cluster.
Saner COPM lets teams create custom benchmarks tailored to specific namespaces and selected security checks, giving greater flexibility in how different workloads are assessed. Instead of applying a single generic standard across every resource, teams can scope compliance checks to match the actual risk profile of each namespace.
Assess System Compliance and Security Posture
See severity distribution and compliance status across every primary benchmark in one place.
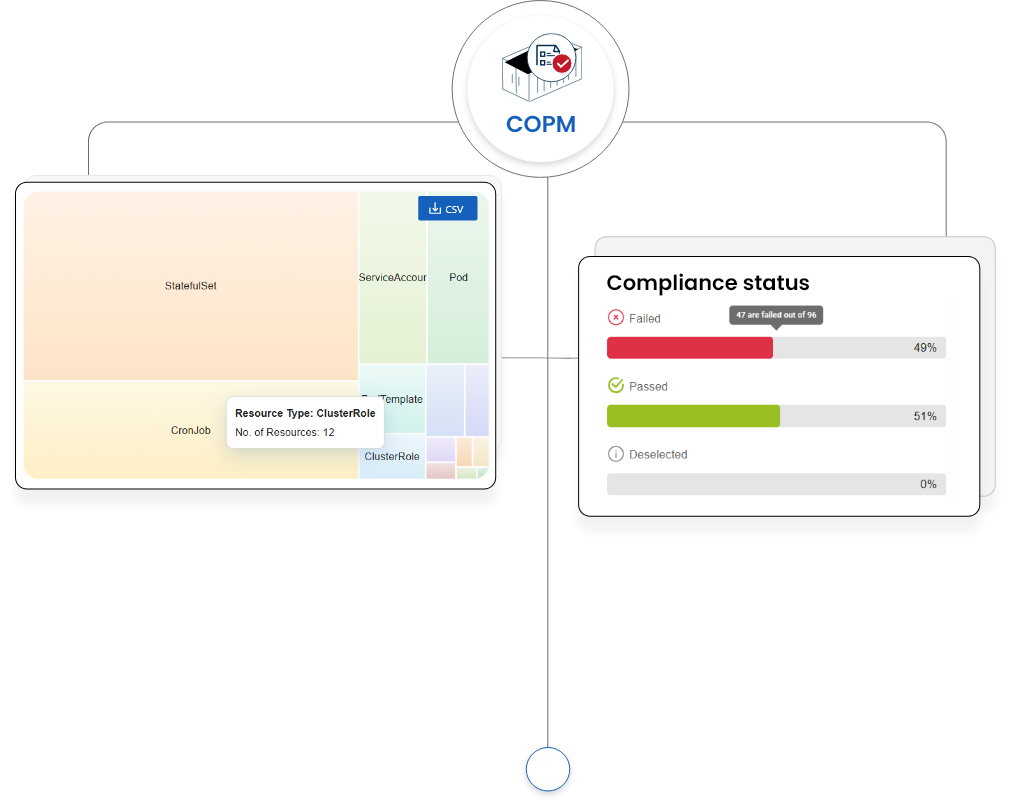
Saner COPM offers a comprehensive overview of primary benchmarks, showing their severity distribution and compliance status. Teams can track which resources have passed, failed, or remain unchecked due to disabled checks or unavailable data, providing a clear and honest understanding of compliance posture rather than a partial view.
Identify and Resolve Configuration Issues With Quick Evaluation Benchmarks
Run fast, focused evaluations during routine audits instead of waiting on a full scan cycle.
Saner COPM offers fast and efficient evaluations of benchmarks, allowing organizations to quickly identify and resolve configuration issues during routine audits. This feature helps save time and ensures continuous compliance with security standards without disrupting existing workflows.
Detect Patterns Over a Period With Resource Trends
Track how resource configurations change over time to catch recurring or worsening issues.
Saner COPM offers a comprehensive overview of primary benchmarks, showing severity distribution and compliance status over time. Teams can see if resources have passed, failed, or remain unchecked due to disabled checks or unavailable data, providing a clear understanding of compliance posture as it evolves rather than a single-point-in-time snapshot.
Connect Findings With Remediation
Move supported COPM findings into the workflow used for corrective action.
Saner COPM operates within Saner COSP, allowing supported findings to connect with Saner CORP for broader risk prioritization and Saner CORM for remediation. Assessment context remains available as teams decide what needs attention and carry corrective work forward.